Secure boot on Nerves, on a CompuLab IOT-DIN-IMX8PLUS
Carrying everything learned on the lab unit into a real, purpose-built Nerves system — without touching the build running in the field.
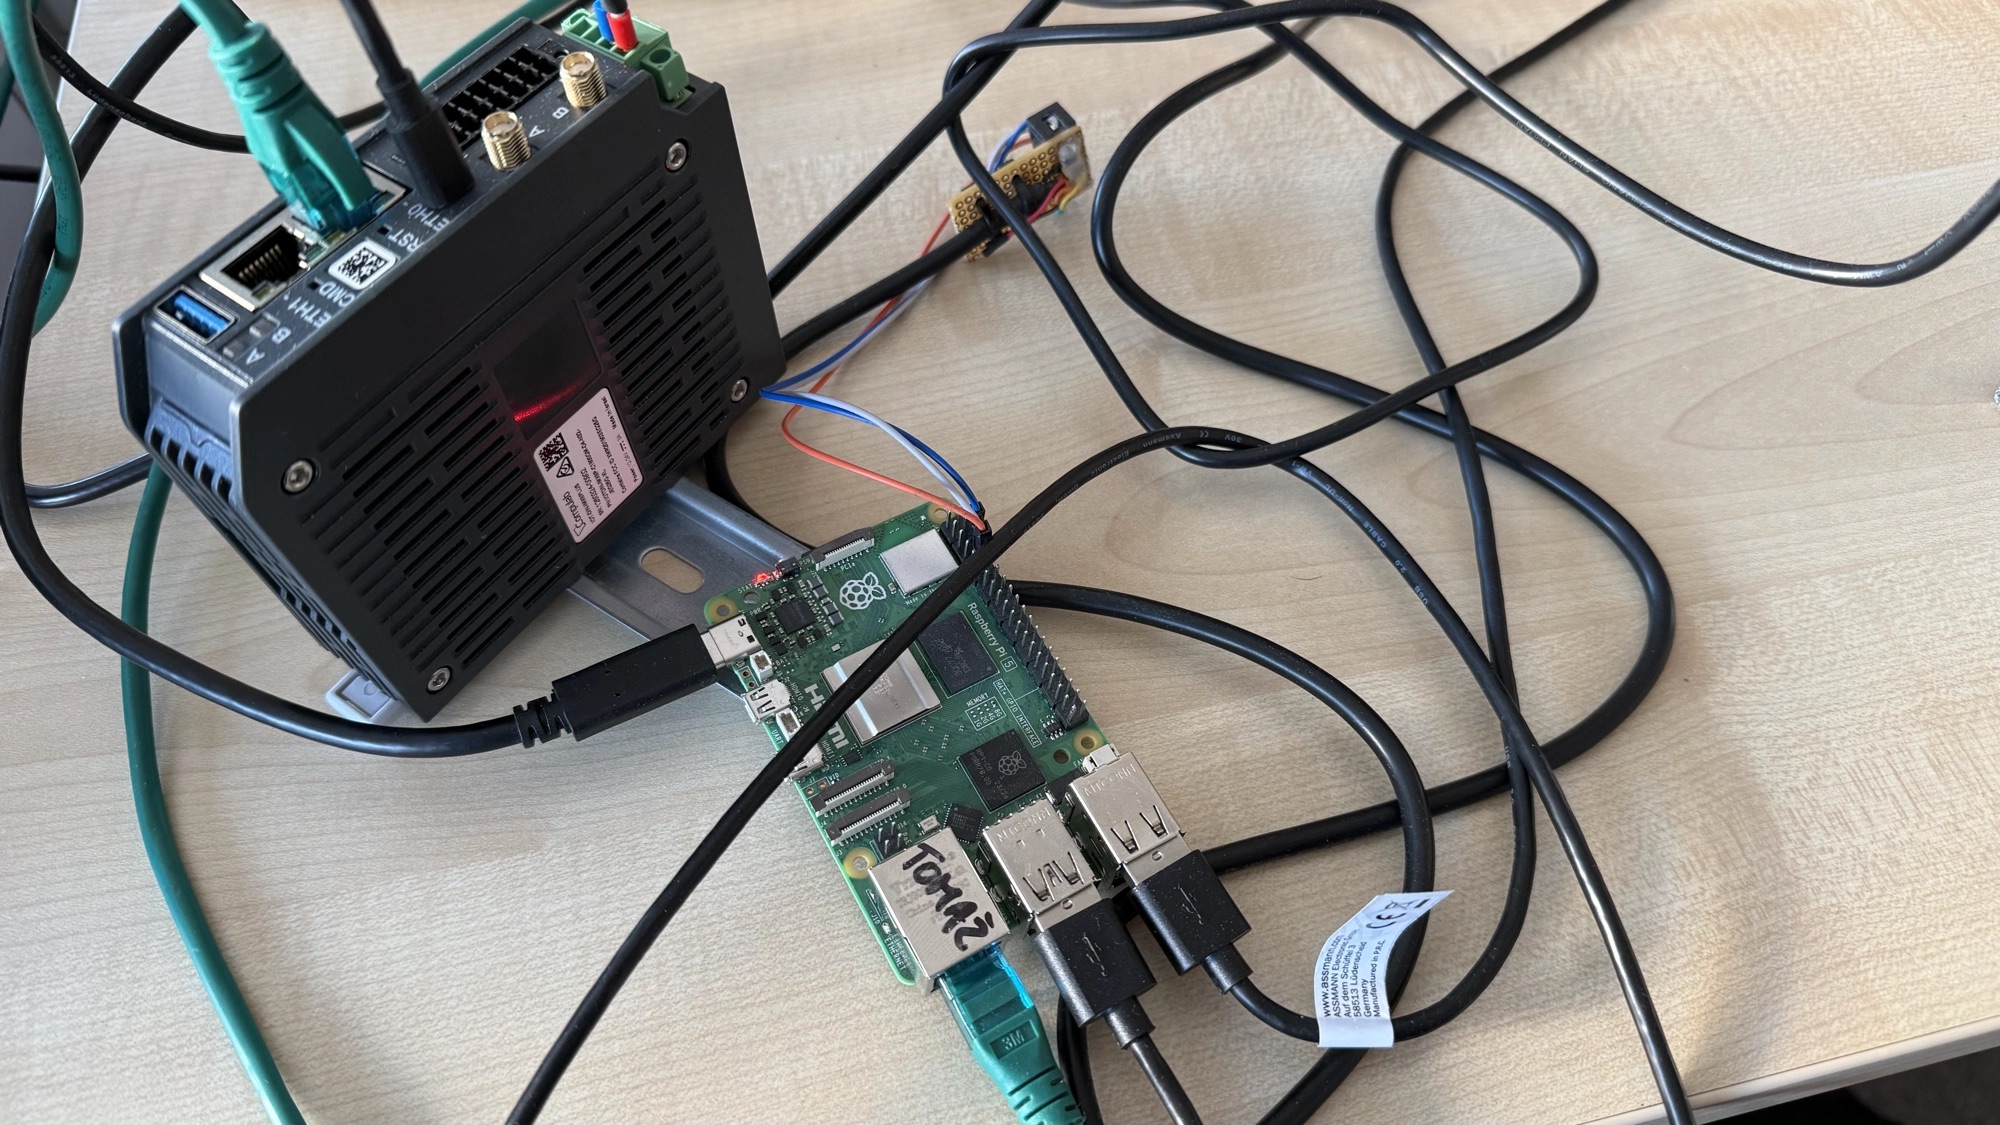
The second half of the project. Same hardware, same lab unit, but now against a real production Nerves system — done in a fork, so the version in the field is never at risk.
From a lab unit to a production Nerves system on the IOT-DIN-IMX8PLUS
The first series proved HAB secure boot on a disposable lab unit running stock Linux. This one carries it into a real Nerves system — in a fork, so the build that runs in the field is never at risk. Same board, different starting point, and several things that do not transfer.
Forking the Nerves system, and enabling HAB inside a Buildroot build
Three real bugs blocked the first three attempts: a nerves package version whose error message points nowhere near the cause, a missing .tool-versions, and the same SPL SRAM overflow track A hit. Plus the arm64 header field that is at offset 0x10, not 0x4.
Signing the Nerves kernel on i.MX8M Plus, clean on the first try
The same kernel-signing procedure as track A, on a different build — and it passed first time, because the two things that went wrong last time were checked rather than assumed. A 691,712-byte padding gap, and a signed range that goes through the IVT.
Making the Nerves build sign imx-boot and the kernel automatically
Wiring signing into the build, and a correction worth more than the wiring: I planned to point fwup.conf at signed artifacts, and that was the wrong layer entirely — the signed bootloader is not in the .fw file at all.
It boots signed — and the HAB gate in booti I did not know I had
The signed Nerves firmware boots. And a finding that deleted an open task: enabling CONFIG_IMX_HAB wires an automatic fail-closed authentication gate into booti itself, for every kernel boot, with no bootcmd changes at all. Plus a fleet gotcha about who can SSH in.